Security Best Practices
Comprehensive security recommendations for your Cafora Minecraft server.
Illustrated procedure
Screenshots show the current application with demonstration data. Use your own service details; click an image to inspect it at full size.
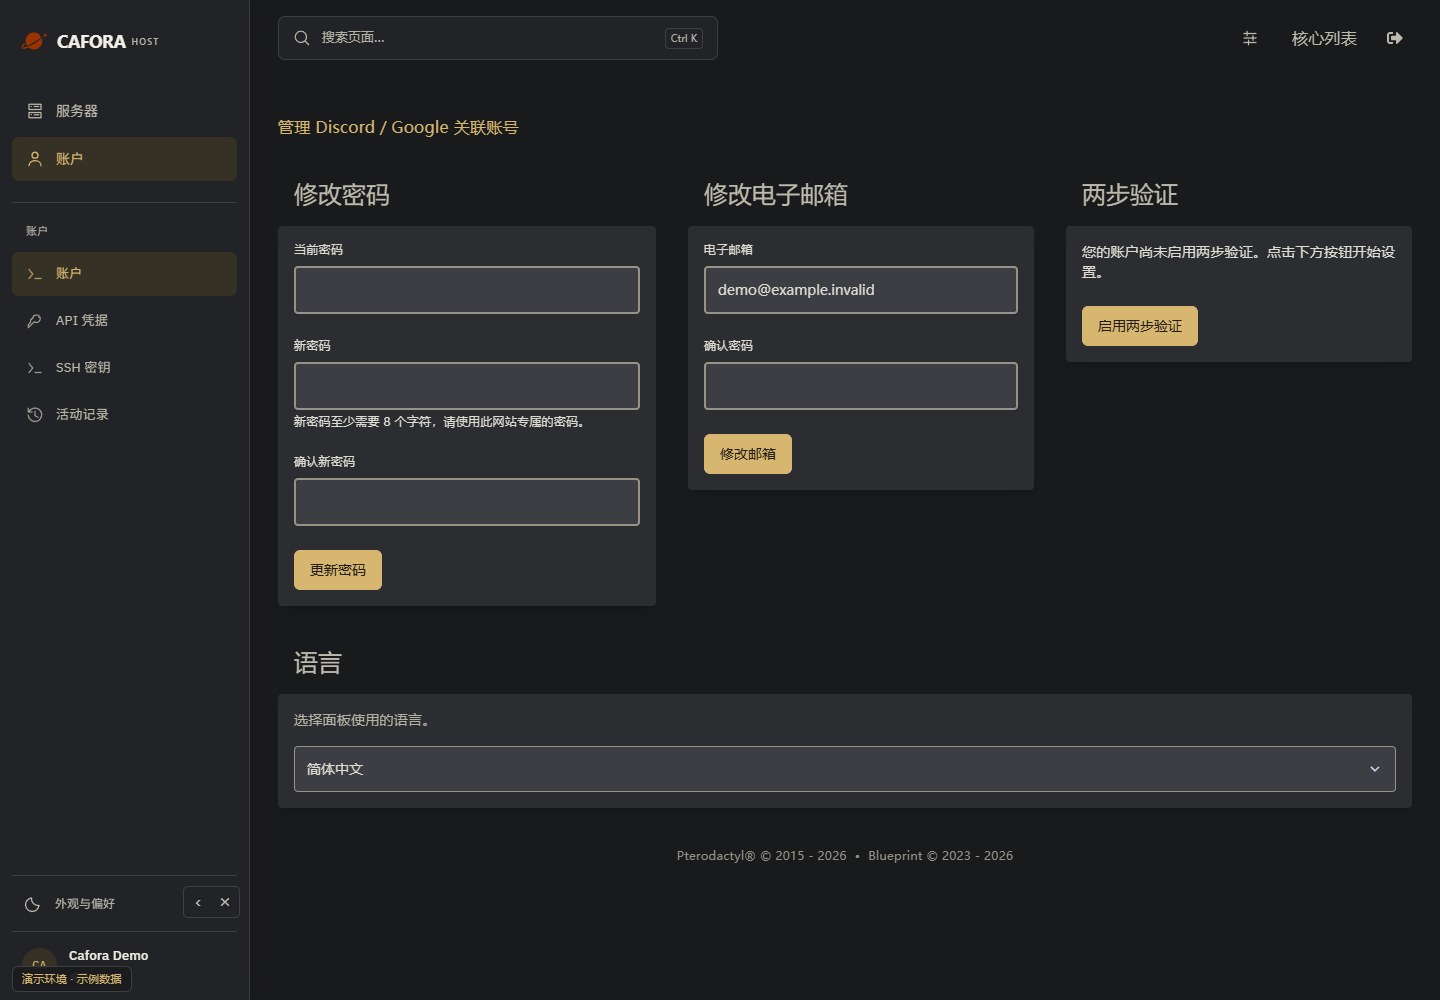
Open account security
Open Account in Panel. Password, email and Two-Step Verification settings belong to this Panel account, not automatically to your Store or DirectAdmin account.
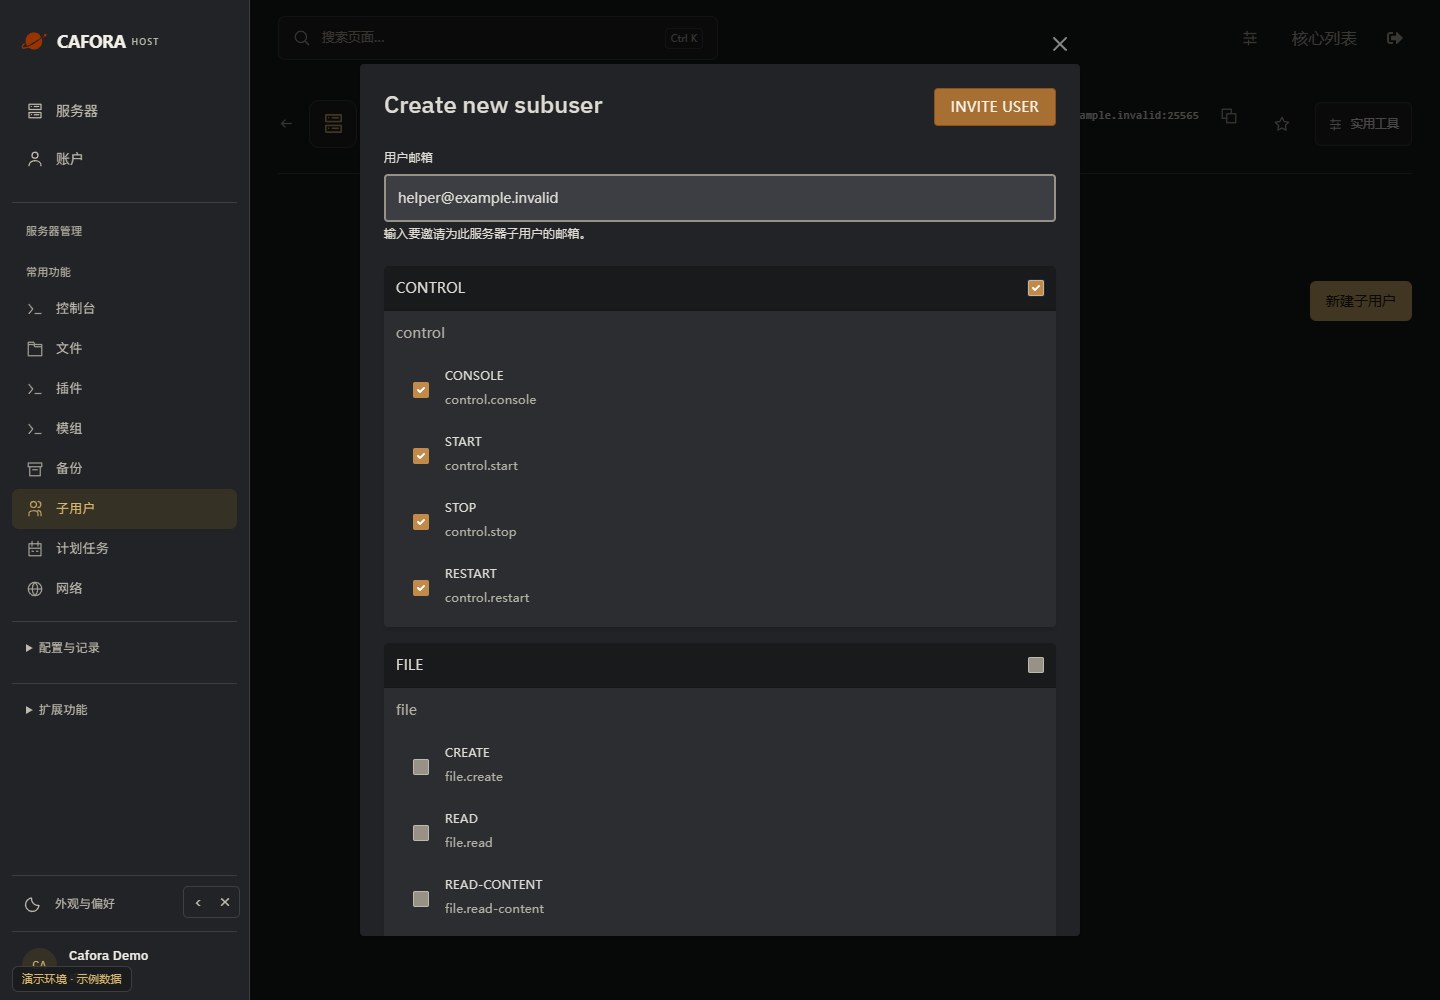
Grant only the required permissions
Review each permission group before sending the invitation. File deletion, restoration, reinstallation and managing users need particular care. Remove access when no longer needed.
Server Security Checklist
- Keep server software updated
- Keep all plugins updated
- Use a permissions plugin instead of OP
- Enable whitelist for private servers
- Configure regular automatic backups
- Monitor server console for suspicious activity
- Use strong passwords for your Cafora account
- Enable 2FA on your Cafora account
- Review firewall rules periodically
- Do not share API keys publicly
- Do not attempt to probe or connect to the origin IP (connections are dropped)
Network-Layer Protection
Cafora handles most of the network attack surface for you at the infrastructure layer:
- Minecraft main game ports use NXEON VPS / WireGuard; SFTP on TCP
2022is also forwarded back to the node through NXEON VPS / WireGuard, with connection details shown in the panel - Panel and API traffic goes through Cloudflare Tunnel
- The origin IP does not accept direct Minecraft / SFTP connections
So your focus should be on application-layer security: plugin vulnerabilities, permission configuration, and account credentials. See DDoS Protection.
Incident Response
If you suspect a security breach:
- Stop the server immediately
- Change your Cafora account password
- Review server logs for unauthorized activity
- Restore from a known-clean backup
- Contact Cafora support